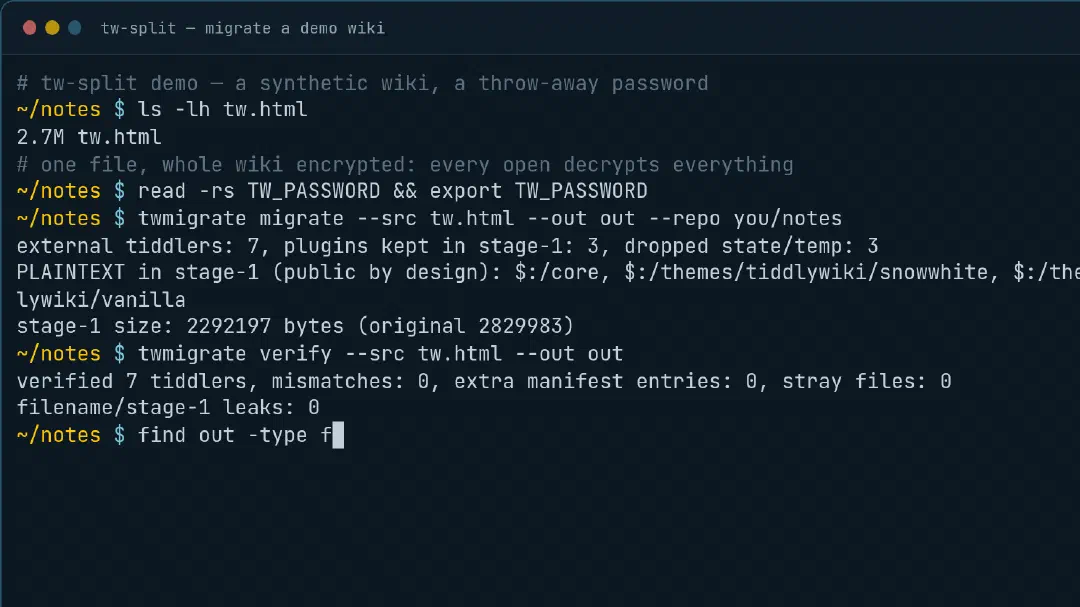
tw-split
Encrypted storage for a TiddlyWiki on GitHub Pages, one AES-256-GCM file per note, loaded only when you open it.
Senior Security Analyst · Cloud & Kubernetes security · ERNW
Reading systems the way attackers do, so others don't have to.
“The enemy knows the system.”
“Cypherpunks write code.”
“Privacy is necessary for an open society in the electronic age.”
> found: 1 trust boundary, 0 checks
“Attacks always get better; they never get worse.”
“You can't trust code that you did not totally create yourself.”
“For a successful technology, reality must take precedence over public relations, for nature cannot be fooled.”
> assumption invalidated
“The Net interprets censorship as damage and routes around it.”
01 · focus
I work in the cloud security team at ERNW. I've reviewed more cloud accounts and container platforms than I can count, on the big public clouds, on sovereign clouds and on just about every Kubernetes distribution.
9+ years of offensive security
| PLATFORM | CATEGORY | REVIEWED |
|---|---|---|
| AWS | public | account review |
| Azure | public | account review |
| Google Cloud | public | account review |
| Alibaba Cloud | public | account review |
| IBM Cloud | public | account review |
| OpenStack | private | account review |
| SAP Converged Cloud | private | account review |
| Cloud Foundry | private | account review |
| EKS | kubernetes | platform review |
| AKS | kubernetes | platform review |
| GKE | kubernetes | platform review |
| OpenShift | kubernetes | platform review |
| Rancher | kubernetes | platform review |
| Gardener | kubernetes | platform review |
| Kubermatic KKP | kubernetes | platform review |
| SAP Kubernikus | kubernetes | platform review |
… and more
How a tenant, subscription or organisation is set up: who can do what, what's exposed to the internet, whether anyone would notice an attack, how keys are handled, and which guardrails are actually enforced.
Kubernetes and PaaS clusters, checked for RBAC, how well tenants are separated, admission control, workload isolation, node and control-plane hardening, and the supply chain.
I've led red-team assessments against cloud and container platforms with realistic attacker goals and a tight scope. The aim is always results the team can actually fix.
Together with Sven Nobis I teach Offensive Kubernetes Security 101 at TROOPERS and as an open training with HM Training Solutions.
Teaching →02 · featured
Encrypted storage for a TiddlyWiki on GitHub Pages, one AES-256-GCM file per note, loaded only when you open it.
03 · log
This shall be a block post submitted via new vault feature
Static HTML, no cookies, no trackers, and an encrypted notebook that doubles as my CMS.
Why I replaced TiddlyWiki's whole-file encryption with one encrypted file per note, and what I learned along the way.
Black- and whitebox techniques for assessing a Puppet Enterprise landscape: exposed status and Jolokia endpoints, CSR auto-signing, client-certificate header bypasses behind TLS termination, mass command execution after compromising the …
04 · teach
Hands-on offensive Kubernetes security trainings at TROOPERS and with HM Training Solutions.
The public version of the offensive Kubernetes training, bookable through HM Training Solutions.
Attack and defend a shared Kubernetes cluster, first through an auditor's eyes, then an attacker's: K8s fundamentals, auditing cluster security, common pitfalls of managed clusters and how clusters get compromised. All exercises run on a shared K3s cluster; the training ends with an attack-and-defence game between participants.
First run of the workshop at TROOPERS: auditing and attacking Kubernetes on a shared K3s cluster, from fundamentals to cluster compromise, ending in an attack-and-defence game.